The AI firewall
for regulated companies.
Launch your dedicated private AI tenant in minutes. Nunc Guardian gates what AI can access, enforces 16 regulatory DLP packs (HIPAA, PCI-DSS, SOX, GDPR, FERPA) plus custom confidential rules, stops prompt injection, and keeps your connected systems safe — whether you bring your own agents or run ours.
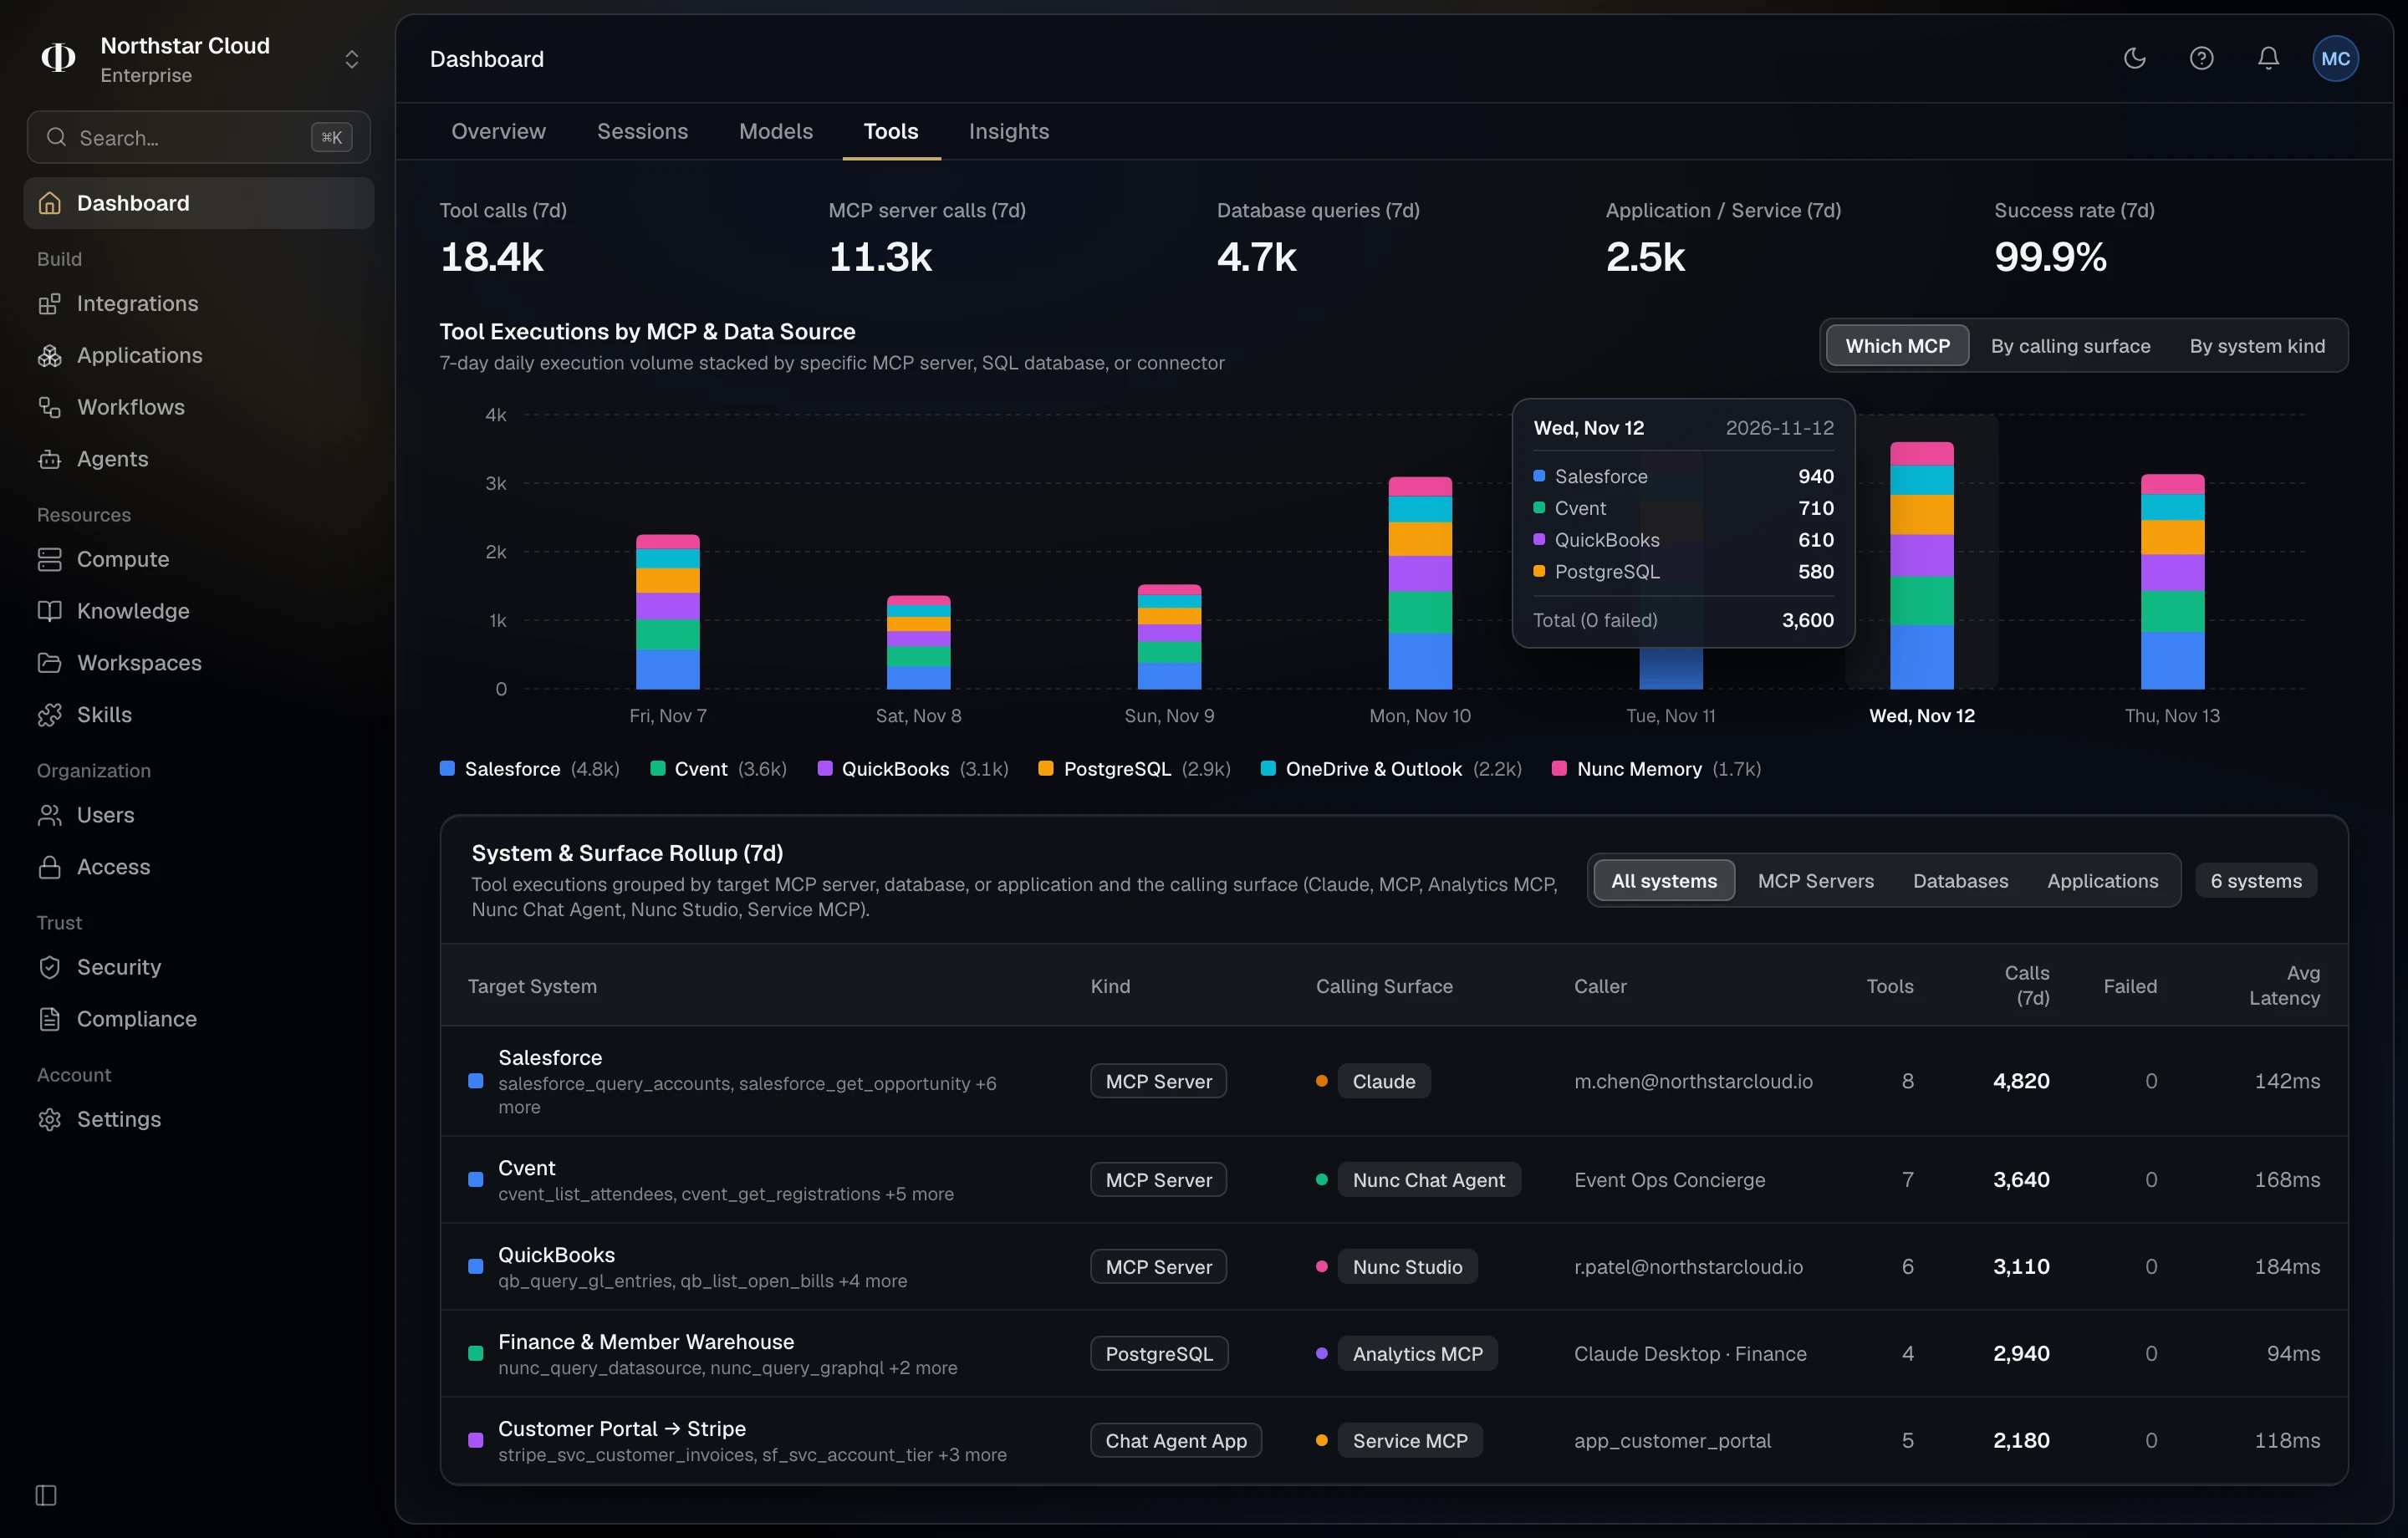
- Records and tool calls processed per month inside isolated boundaries
- 2B+
- Records and tool calls processed per month inside isolated boundaries
- Dedicated tenant isolation — zero shared tables or training logs
- 100%
- Dedicated tenant isolation — zero shared tables or training logs
- Unapproved writes or raw PII and PHI exposed to external models
- 0
- Unapproved writes or raw PII and PHI exposed to external models
- To deploy your governed AI cloud, not months of custom build
- Minutes
- To deploy your governed AI cloud, not months of custom build
Connect your agents — or run ours across everything you own.
Our protocol isn't the story; what it unlocks safely is. Plug in your favorite AI assistant, embed into your client app, or launch Nunc Private Agents.
Keep the AI clients your team already uses
Point external assistants and custom apps at Nunc with OAuth 2.1 SSO. Guardian enforces access gates, PII masking, and human write approvals on every call.
 Claude
 ChatGPT
 Cursor
 Gemini
 VS CodeSDK@nunc/sdk
Run Nunc Private Agents & Data Studio
Deploy private specialist agents, query live warehouses in plain English in Data Studio, or embed customer-facing AI assistants directly into your product or portal.
 Postgres
 Neon
 Supabase
 Amazon RDS
 Snowflake
 BigQuery
 ClickHouse
 DuckDB
 MotherDuck
 SQLiteCSVCSV
 Parquet
 Salesforce
 Sage Intacct
 QuickBooks
 Bill.com
 Expensify
 Stripe
 Cvent
 Gmail
 Outlook
 Microsoft Teams
 Zoom
 Slack
 Google Calendar
 Asana
 Jira
 BambooHR
 Greenhouse
 Figma
 Canva
 Adobe Creative Cloud
 Whimsical
 Onshape3D3D Modeling
 Esri ArcGIS
 Mapbox
 HERE
 TomTom
 Geotab
 StreetLight Data
 Census TIGER
 FHWA HPMSIMGImage GenerationVIDVideo GenerationAUDAudio Generation
 OneDriveMDMarkItDownWSWeb SearchMGMemory GraphISOISO 27001CVEVulnerability Intel
 Git
 GitHubGRCode Search
 Playwright
Already built an MCP server? Federate it through Nunc Console to wrap it in Guardian DLP, corporate SSO, and ISO 42001 audit logs.
Guardian gates what AI touches — with 16 regulatory DLP packs and query guards built in.
Inspect how Nunc blocks prompt, SQL, GraphQL, graph, and regex injection while enforcing HIPAA, PCI-DSS, SOX, GDPR, FERPA, and custom confidential rules across every query, tool call, code sandbox, and authenticated browser session.
Control what AI can read — and require a person to approve changes.
Every assistant starts with zero access. You choose which apps, tables, and folders each team or client can read, mask sensitive fields automatically before any model sees them, and hold real-world changes for human sign-off.
- Permissions follow each signed-in employee, team, or customer account
- Names, SSNs, medical IDs, and bank numbers are masked before AI inference
- Sending emails, updating records, or posting entries pauses for human approval
- AllowedRead approved finance & CRM recordsPermitted for authorized roles · restricted tables stay hidden
- MaskedSensitive donor, patient & client fieldsNames, SSNs, and account numbers masked before reaching AI
- Human ApprovalPost journal entry or send external emailPaused with a plain-English summary until a manager approves
- BlockedUnapproved apps, payroll, or admin settingsRefused automatically before the request touches your systems
Stop prompt, SQL, GraphQL, graph, and regex attacks before execution.
Even when an assistant has permission to answer questions, Guardian inspects every instruction, tool call, and generated query inline — stopping hidden prompt hijacks and unsafe database or search patterns before they reach your systems.
- Catches hidden instructions tucked inside emails, documents, tickets, and web pages
- Blocks unsafe SQL, GraphQL, and graph queries that try to dump or alter data
- Stops runaway regex patterns and bulk scraping before they slow down connected tools
- BlockedPrompt & indirect injectionHidden 'ignore prior rules' traps inside emails, PDFs, or web pages
- BlockedSQL & GraphQL injectionAttempts to bypass user row filters, export schemas, or delete records
- BlockedGraph & relationship traversal abuseUnauthorized cross-account hops or runaway deep-link queries
- BlockedRegex injection & search overloadCrafted search patterns designed to freeze or scrape connected apps
Enforce HIPAA, PCI-DSS, SOX, GDPR, FERPA, and custom rules out of the box.
Turn on industry and regional compliance packs in Nunc Console, or add plain-language rules for confidential deals, board memos, and internal project names — choosing per rule whether to block, mask, or log an audit warning.
- 16 built-in regulatory packs across healthcare, finance, education, legal, and privacy
- Custom confidential rules protect deal codenames, M&A drafts, and sensitive topics
- Feeds live compliance proof into ISO/IEC 42001 and ISO/IEC 27001 reports
- MaskedHealthcare & student records (HIPAA · FERPA)Clinical notes, medical IDs, and transcripts masked before AI reads them
- ProtectedPayments, banking & audit data (PCI-DSS · SOX · GLBA)Card numbers, routing details, and pre-release financials kept private
- EnforcedGlobal privacy laws (GDPR · CCPA · PIPEDA · LGPD)Regional national, health, and tax identifiers protected across borders
- Block or WarnCustom confidential topics & deal namesPlain-English rules for M&A codenames, board memos, or legal privilege
Automate web portals without exposing logins or obeying malicious pages.
When a system has no API, Nunc runs authenticated browser tasks inside a disposable container — signing in without showing passwords or cookies to the AI, scrubbing hidden page attacks, and asking a person before submitting forms.
- Agents never see raw passwords, session cookies, or authentication tokens
- Restricts browsing to approved business domains and strips hidden page traps
- Submitting forms, payments, or portal updates requires human sign-off
- Login HiddenPortal sign-in & stored credentialsApplied privately inside the container — never visible to the AI
- ScrubbedReading portal pages & statementsHidden page traps removed and account or health IDs masked on read
- Human ApprovalSubmitting forms, payments, or updatesHolds before clicking submit until an authorized teammate approves
- BlockedUnapproved websites & external linksNavigation outside your approved domain list is refused automatically
Run exact reconciliations and spreadsheet checks in a locked workspace.
Instead of letting an AI guess at numbers, Nunc runs calculations, CSV checks, and reconciliations inside a sealed temporary container — with zero access to your live databases, company passwords, or outside networks.
- Exact math and variance checks across thousands of rows — no AI rounding errors
- Sealed off from live databases, stored API keys, and unapproved websites
- Temporary workspace and scratch files automatically wipe clean within 24 hours
- Exact MathLedger & spreadsheet reconciliationDeterministic totals and tie-outs across CSVs, exports, and statements
- Private OutputCharts, summaries & clean exportsGenerates verified reports inside your organization's private tenant
- Air-GappedLive databases & stored passwordsSandbox has zero network path to production systems or secret vaults
- Auto-PurgedTemporary working filesAutomatically deleted after completion (24-hour maximum lifetime)
Answer questions from live databases without copying tables to a third party.
Connect Snowflake, BigQuery, Postgres, or spreadsheets inside your own dedicated Nunc Private Cloud. Questions run where your data already sits, sensitive columns stay masked, and zero records are ever used to train AI models.
- Physically separate database, memory, and file vault per organization — nothing shared
- Queries run where your data already lives without expensive data-copy pipelines
- Zero customer prompts, files, or results ever retained in AI training logs
- In-Place ReadSnowflake, BigQuery & PostgresQueried directly where your data sits — no third-party warehouse copies
- User-ScopedPer-person table & row visibilityEmployees and clients only see the tables and rows assigned to them
- Isolated TenantOrganization database, memory & vaultDedicated per-customer storage boundary with zero shared tables
- Never Trained OnExternal AI model training logsPrompts, documents, and query results are never used to train models
Allow, user-scope, or block every table before an agent runs.
Select which warehouse tables an agent can query, bind rows automatically to the signed-in user, or block sensitive schemas at the SQL AST guard.
High-trust organizations — with or without an AI team.
Organizations that steward sensitive records, answer to a board or regulator, and want out-of-the-box private AI in minutes without hiring an infrastructure team.
- Associations & non-profitsmembership · foundations · grants · the 990
- Finance & accountingQuickBooks · Intacct · Bill.com · close & reconciliation
- Legal & compliance16 DLP packs · PII masking · ISO 42001 & 27001
- Civil, E&G & geospatialpublic sector · transport · infrastructure · mapping
- Client-facing SaaS & portalscustomer portals · @nunc/sdk · per-account isolation
- HR & enterprise operationsonboarding · federated MCPs · browser portals
For the people who will ask how.
The architecture behind the guarantees — physical isolation, data boundaries, model routing, and operational memory. Explore Nunc Private Cloud.
- Nunc Private Cloud
- dedicated gateway, database, vector memory, storage, and audit ledger — zero shared tables or training logs
- Nunc Guardian inline
- gates AI access, blocks prompt, SQL, GraphQL, graph & regex injection, enforces 16 DLP packs, and holds writes for human approval
- Nunc Private Agents
- role-scoped specialist agents you can delegate multi-step work to — with workspace isolation and human write gates
- Company Knowledge
- 4-tier vector memory (Public, Company, Workspace, and Agent) scoped per tenant and scrubbed before recall
- Your data stays put
- Postgres, Snowflake, BigQuery queried in place without expensive ETL or integration middleware
- It learns how you operate
- background loops turn operational outcomes into tenant-private rules the planner honors next time
Launch your private AI in minutes — without giving up your data.
Start a 14-day isolated Core Platform trial with $0 due today, inspect Guardian live, or speak with our team about a custom deployment.