Console & Gatewaysconsole.nunc.cloud · 15-Minute Admin Runbook
Console Setup & RBAC
https://console.nunc.cloud is the control plane for identity, connectors, warehouse table scoping, default-deny tool permissions, Guardian PII policies, and compliance audit exports.
1. Initial tenant setup checklist (15 minutes)
- Bind SSO & SCIM groups (Organization → Users): Connect Okta, Microsoft Entra ID, or Google Workspace and map employees into functional groups (Finance, RevOps, Engineering). Assign Console roles (
Admin,Builder,Member). - Create Workspaces (Resources → Workspaces): Set up department workspaces (e.g.
finance-close), attach curated Knowledge collections, and optionally pair Slack or Microsoft Teams channels. - Connect SaaS & SQL warehouses (Build → Integrations): Enable SaaS apps (Outlook, Salesforce, Sage Intacct) and bind read-only Snowflake/PostgreSQL credentials. On each database, set table policies to
Allow Agent,Scope to User, orBlock. - Grant default-deny PBAC rules (Organization → Access): Set read tools (
list_*,get_*) to Allow, mutating tools (send_*,create_*,update_*) to Gate, and destructive tools (*_delete_*) to Deny. - Set Guardian privacy & egress rules (Trust → Security): Choose
Strict,Medium, orPermissive, verify your 17 PII categories, and allowlist approved outbound domains. - Set approved models, budgets & MDM lock (Account → Settings): Configure per-user/org token budgets and optionally export Claude Enterprise Lock JSON files for workstation MDM deployment.
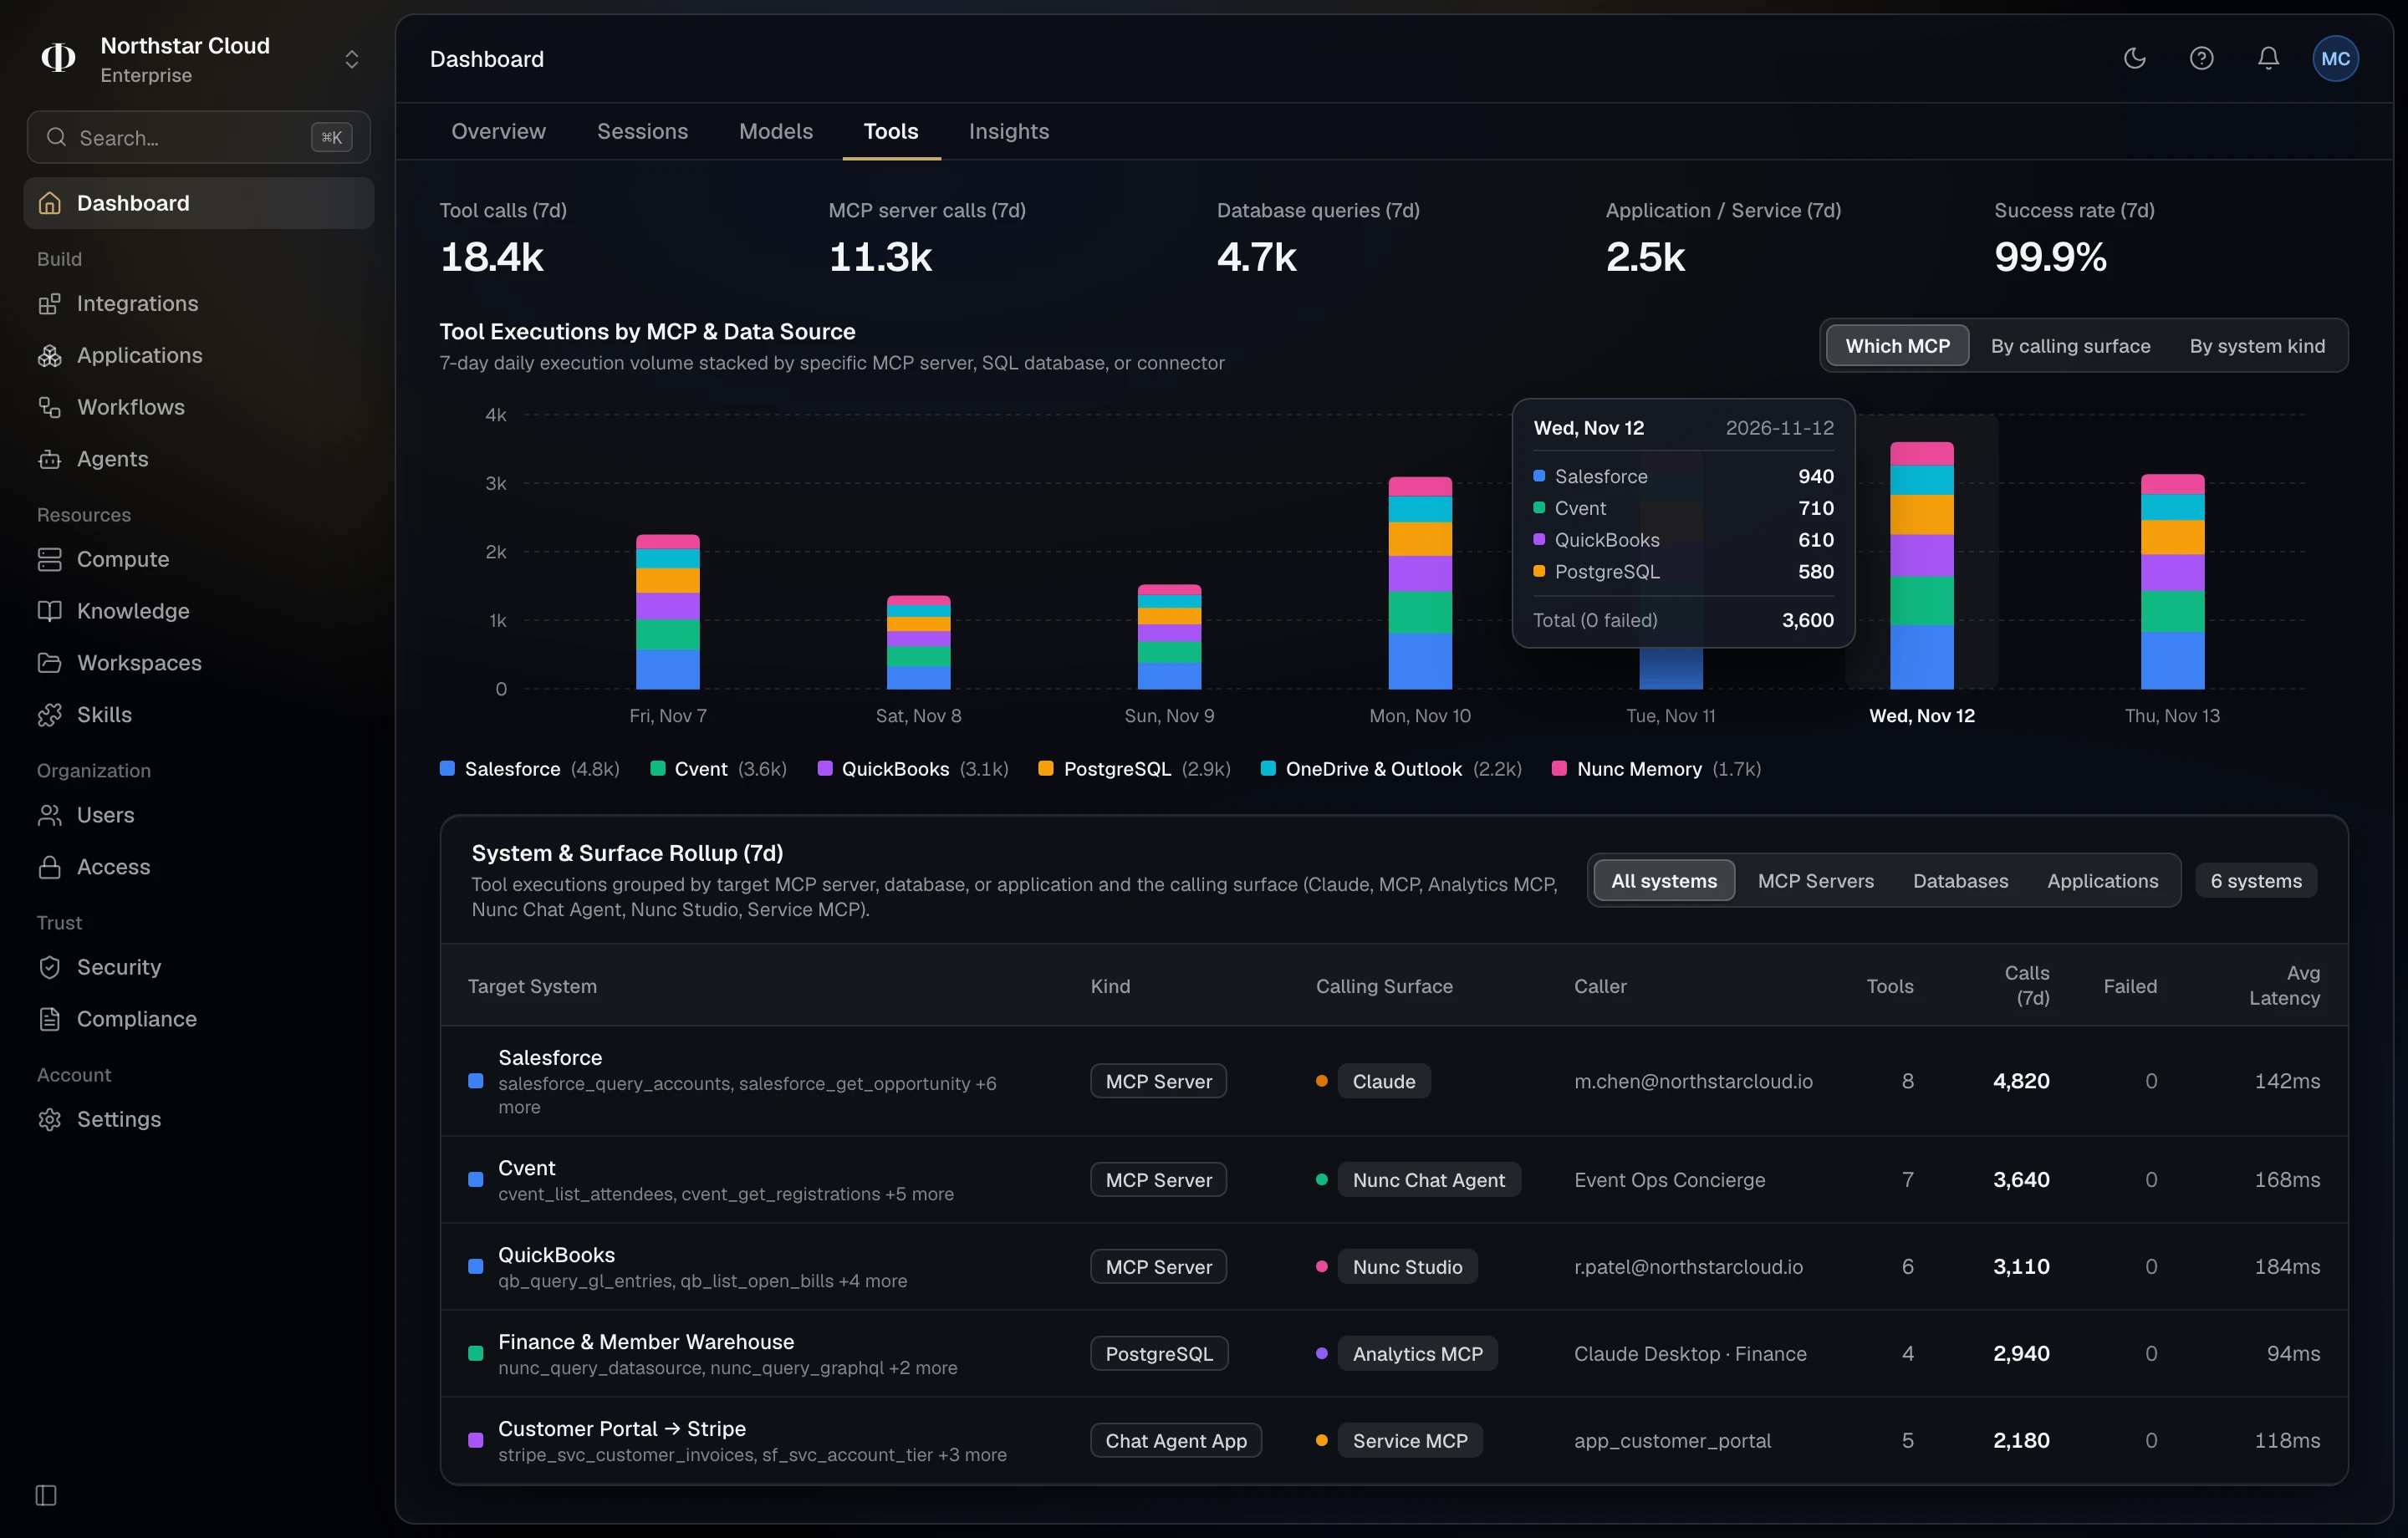
2. Day-2 operational & incident controls
- Emergency Kill Switches (Trust → Security): Pause external MCP access, third-party SaaS writes, or a specific connector tenant-wide in one click during an incident or drill.
- Pending Write Approvals (Trust → Security): Review and approve or reject SHA-256 payload-locked write requests held by Guardian Stage 3.
- Audit Export & ISO/IEC 42001 Evidence (Trust → Compliance): Export tamper-evident SHA-256 audit logs and fulfill data-subject deletion requests across conversation and memory stores.
Related: Console Surface Map · How Nunc Configuration Works