Nunc GuardianSensitivity Tiers · PII Tokenization · PBAC · Egress Allowlists
Configure Guardian Firewall
Configure Nunc's inline 6-stage AI firewall in Console → Trust → Security. Models never hold standing credentials and never receive raw regulated PII unless explicitly permitted by your tenant policy.
1. Step-by-step configuration in Console
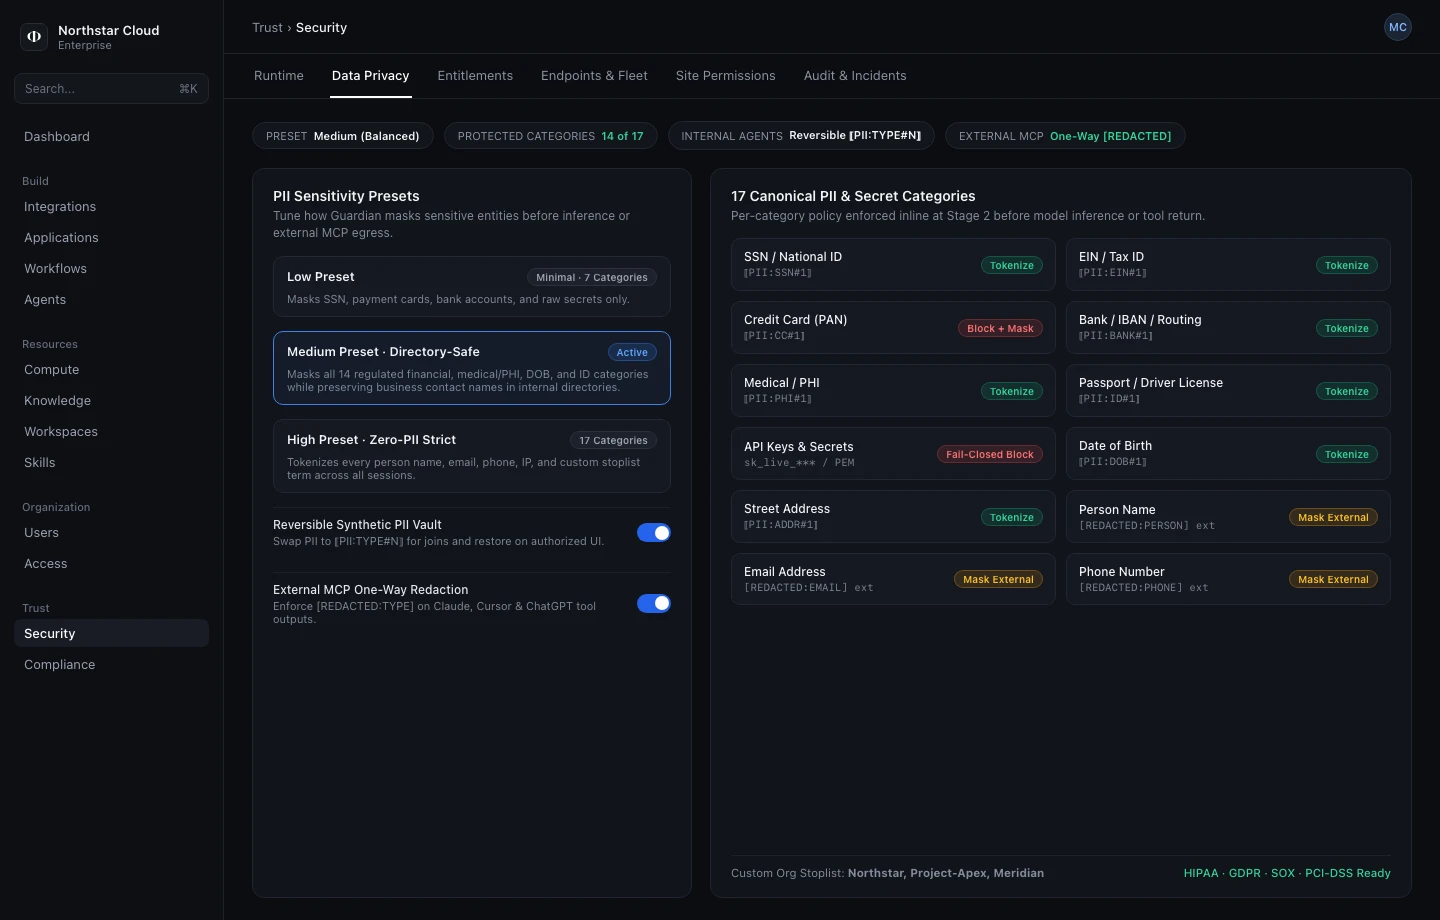
- Select a Sensitivity Tier (Trust → Security → Data Privacy): Choose
Strict(regulated HIPAA/PCI/Legal — masks all 17 PII/PHI detectors and gates all writes),Medium(enterprise default — masks SSN, payment cards, MRN, credentials, emails, and phones), orPermissive(blocks secrets and jailbreaks in internal engineering workspaces). - Toggle PII detectors & add custom regex: Enable or disable individual built-in categories and register custom regex patterns (for example, internal patient MRN formats, claim numbers, or deal codes).
- Configure Multi-Tier DLP & Custom Compliance Rules (Data Privacy → DLP & Regulatory Packs): Apply vertical presets or toggle any of the 16 Tier 1 Industry (PCI-DSS, HIPAA, SOX, GLBA, FERPA, COPPA, CUI / 800-171, Legal/IP) and Tier 2 Regional (GDPR, CCPA/CPRA, PIPEDA, UK GDPR, LGPD, APPI/PDPA, FINRA MNPI) packs, add custom
{ Name, Description, Action }rules (`Block Turn`, `Tokenize / Redact`, or `Audit Warn`), and verify rules live in the Inline DLP Policy Tester. - Set outbound egress allowlists (Trust → Security → Site Permissions): Add approved corporate domains for webhooks, web-fetch, and governed browser sessions. Guardian blocks unlisted outbound HTTP destinations and hidden markdown image beacons.
- Configure write-approval channels: Route
409 Awaiting Approvalgates to Console approvers or a dedicated Slack/Teams approval channel.
2. How PII masking differs by surface
- Reversible Tokenization (Data Studio Web): Models reason over deterministic placeholders such as
⟦PII:EMAIL#1⟧or⟦PII:SSN#1⟧. Nunc re-hydrates cleartext values only inside the authorized user's browser session — external foundation model providers never receive raw PII. - One-Way Redaction (External MCP Clients): When Claude Desktop, ChatGPT, Gemini, or Cursor calls
/mcpor/mcp/analytics, Guardian emits irreversible[REDACTED:TYPE]masks so raw PII never enters third-party AI vendor logs.
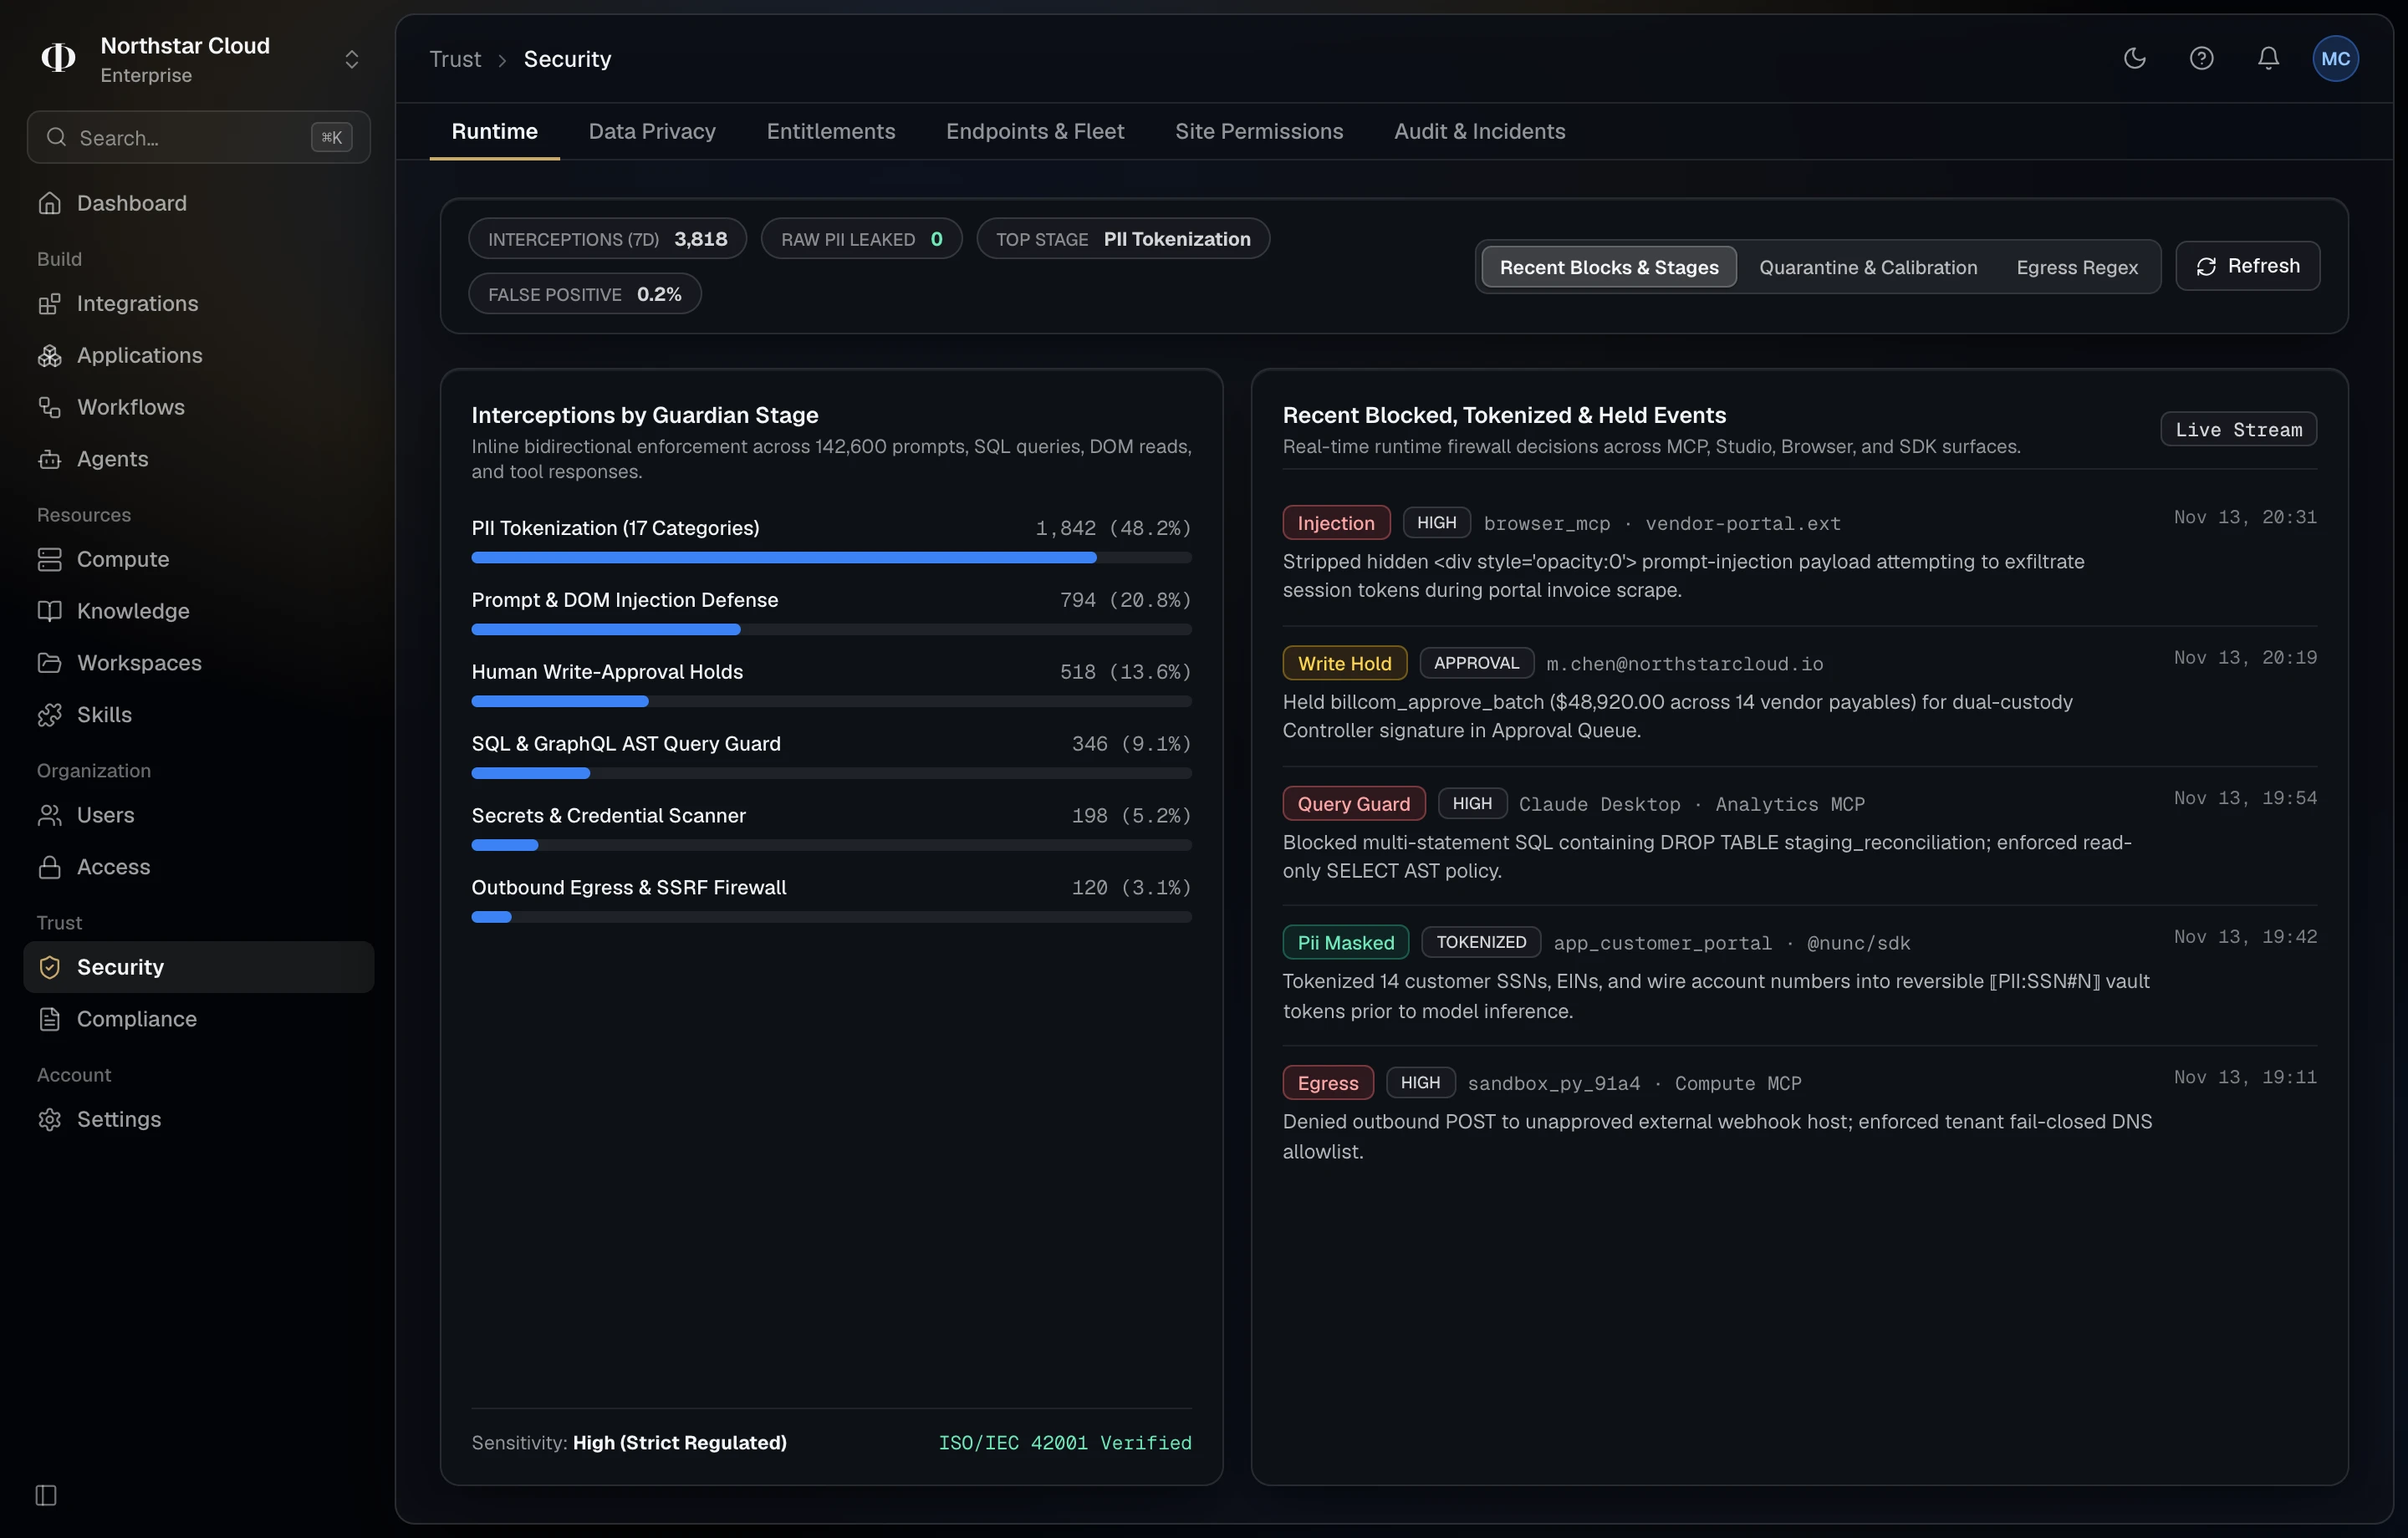
3. Reference: The 6-stage Guardian pipeline
| Stage | Runtime Enforcement |
|---|---|
| 1. Input Inspection | Scans user prompts, channel messages, and retrieved chunks for prompt injection, jailbreak heuristics, and restricted topics before model inference. |
| 2. Privacy & Secret Tokenization | Replaces PII with reversible session tokens (⟦PII:TYPE#N⟧) in Data Studio, redacts PII as [REDACTED:TYPE] on external MCP responses, and blocks leaked credentials. |
| 3. Tool Policy & Approval Gate | Evaluates default-deny PBAC (User > Group > Organization), enforces egress domain allowlists, and pauses mutating tools for SHA-256 payload-locked human approval. |
| 4. Output & Egress Sanitization | Inspects tool payloads, SQL ASTs, and completions to block exfiltration, markdown image beacons, and unapproved outbound URLs. |
| 5. Grounding & Citation Check | Verifies numerical and factual claims against retrieved warehouse rows, tool outputs, and cited tenant documents. |
| 6. Immutable Ledger & Telemetry | Writes tamper-evident execution, policy, and approval records to your tenant audit log and surfaces posture alerts in Console. |
4. Physical tenant isolation & encryption
- Dedicated physical stores per tenant: Every organization receives its own isolated relational database, dedicated vector index, and separate encrypted artifact namespace — never commingled in shared multi-tenant tables.
- Zero training on customer data: Prompts, schemas, query results, and documents are never used to train foundation models.
- TLS 1.3 & envelope encryption: All client, MCP, and Sidecar traffic requires TLS 1.3; connector tokens are encrypted with per-tenant keys.
Related: Guardian Overview · Tool Policies & PBAC · ISO/IEC 42001 AIMS Controls